

Pass Microsoft SC-100 Actual Free Exam Q&As Updated Dump Sep 22, 2026
Latest SC-100 Actual Free Exam Updated 298 Questions
Microsoft SC-100 Exam Practice Test Helps You Ace Your Microsoft Cybersecurity Architect
Passing the Microsoft SC-100 exam is no easy feat. It requires a great deal of preparation, knowledge, and experience. However, you can use our free practice test to help you prepare for it. Our practice exams are written by our own team of subject matter experts and provide a practical approach to learning concepts. In addition, they are updated regularly so that they always reflect the latest version of the exam.
Our SC-100 Dumps include questions that are similar in format and content to actual exam questions. This allows you to become familiar with how real exams look like and how they are scored. You can also use this opportunity to assess your performance against different types of questions so that you can focus on improving those areas where you need improvement.
We offer free access to all of our practice exams for one year from the date of purchase or registration. After this period expires, you will need to pay $9.99 per month in order to continue using them.
NEW QUESTION # 152
Your company is migrating data to Azure. The data contains Personally Identifiable Information (Pll). The company plans to use Microsoft Information Protection for the Pll data store in Azure. You need to recommend a solution to discover Pll data at risk in the Azure resources.
What should you include in the recommendation? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Graphical user interface, text, application Description automatically generated
Prioritize security actions by data sensitivity, https://docs.microsoft.com/en-us/azure/defender-for-cloud
/information-protection. As to Azure SQL Database Azure SQL Managed Instance Azure Synapse Analytics (Azure resources as well): https://docs.microsoft.com/en-us/azure/azure-sql/database/data-discovery-and- classification-overview?view=azuresql
NEW QUESTION # 153
Your company is moving a big data solution to Azure.
The company plans to use the following storage workloads:
* Azure Storage blob containers
* Azure Data Lake Storage Gen2
* Azure Storage file shares
* Azure Disk Storage
Which two storage workloads support authentication by using Azure Active Directory (Azure AD)?
Each correct answer presents a complete solution. NOTE: Each correct selection is worth one point.
- A. Azure Data Lake Storage Gen2
- B. Azure Disk Storage
- C. Azure Storage blob containers
- D. Azure Storage file shares
Answer: A,C
NEW QUESTION # 154
Your company has an Azure App Service plan that is used to deploy containerized web apps. You are designing a secure DevOps strategy for deploying the web apps to the App Service plan. You need to recommend a strategy to integrate code scanning tools into a secure software development lifecycle. The code must be scanned during the following two phases:
Uploading the code to repositories Building containers
Where should you integrate code scanning for each phase? To answer, select the appropriate options in the answer area.
Answer:
Explanation:
Explanation:
https://docs.github.com/en/enterprise-cloud@latest/get-started/learning-about-github/about-github-advanced- security
https://microsoft.github.io/code-with-engineering-playbook/automated-testing/tech-specific-samples/azdo- container-dev-test-release/
NEW QUESTION # 155
You have an Azure subscription that contains an Azure Synapse Analytics workspace named workspace1.
workspace1 contains a built-in serverless SQL pool and a dedicated SQL pool named Pool1.
You need to recommend a second layer of data encryption for workspace1.
What should you include in the recommendation for each pool? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
NEW QUESTION # 156
You have a Microsoft 365 subscription
You need to recommend a security solution to monitor the following activities:
* User accounts that were potentially compromised
* Users performing bulk file downloads from Microsoft SharePoint Online What should you include in the recommendation for each activity? To answer, drag the appropriate components to the correct activities. Each component may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each Correct selection is worth one Point.
Answer:
Explanation:
NEW QUESTION # 157
Your on-premises network contains an e-commerce web app that was developed in Angular and Nodejs. The web app uses a MongoDB database. You plan to migrate the web app to Azure. The solution architecture team proposes the following architecture as an Azure landing zone.
You need to provide recommendations to secure the connection between the web app and the database. The solution must follow the Zero Trust model. Solution: You recommend creating private endpoints for the web app and the database layer. Does this meet the goal?
- A. Yes
- B. No
Answer: B
NEW QUESTION # 158
You need to recommend a multi-tenant and hybrid security solution that meets to the business requirements and the hybrid requirements. What should you recommend? To answer, select the appropriate options in the answer are a. NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Topic 2, Fabrikam, Inc
Overview
Fabrikam, Inc. is an insurance company that has a main office in New York and a branch office in Paris.
On-premises Environment
The on-premises network contains a single Active Directory Domain Services (AD DS) domain named corp.fabrikam.com.
Azure Environment
Fabrikam has the following Azure resources:
* An Azure Active Directory (Azure AD) tenant named fabrikam.onmicrosoft.com that syncs with corp.fabnkam.com
* A single Azure subscription named Sub1
* A virtual network named Vnet1 in the East US Azure region
* A virtual network named Vnet2 in the West Europe Azure region
* An instance of Azure Front Door named FD1 that has Azure Web Application Firewall (WAR enabled
* A Microsoft Sentinel workspace
* An Azure SQL database named ClaimsDB that contains a table named ClaimDetails
* 20 virtual machines that are configured as application servers and are NOT onboarded to Microsoft Defender for Cloud
* A resource group named TestRG that is used for testing purposes only
* An Azure Virtual Desktop host pool that contains personal assigned session hosts All the resources in Sub1 are in either the East US or the West Europe region.
Partners
Fabrikam has contracted a company named Contoso, Ltd. to develop applications. Contoso has the following infrastructure-.
* An Azure AD tenant named contoso.onmicrosoft.com
* An Amazon Web Services (AWS) implementation named ContosoAWS1 that contains AWS EC2 instances used to host test workloads for the applications of Fabrikam Developers at Contoso will connect to the resources of Fabrikam to test or update applications. The developers will be added to a security Group named Contoso Developers in fabrikam.onmicrosoft.com that will be assigned to roles in Sub1.
The ContosoDevelopers group is assigned the db.owner role for the ClaimsDB database.
Compliance Event
Fabrikam deploys the following compliance environment:
* Defender for Cloud is configured to assess all the resources in Sub1 for compliance to the HIPAA HITRUST standard.
* Currently, resources that are noncompliant with the HIPAA HITRUST standard are remediated manually.
* Qualys is used as the standard vulnerability assessment tool for servers.
Problem Statements
The secure score in Defender for Cloud shows that all the virtual machines generate the following recommendation-. Machines should have a vulnerability assessment solution.
All the virtual machines must be compliant in Defender for Cloud.
ClaimApp Deployment
Fabrikam plans to implement an internet-accessible application named ClaimsApp that will have the following specification
* ClaimsApp will be deployed to Azure App Service instances that connect to Vnetl and Vnet2.
* Users will connect to ClaimsApp by using a URL of https://claims.fabrikam.com.
* ClaimsApp will access data in ClaimsDB.
* ClaimsDB must be accessible only from Azure virtual networks.
* The app services permission for ClaimsApp must be assigned to ClaimsDB.
Application Development Requirements
Fabrikam identifies the following requirements for application development:
* Azure DevTest labs will be used by developers for testing.
* All the application code must be stored in GitHub Enterprise.
* Azure Pipelines will be used to manage application deployments.
* All application code changes must be scanned for security vulnerabilities, including application code or configuration files that contain secrets in clear text. Scanning must be done at the time the code is pushed to a repository.
Security Requirement
Fabrikam identifies the following security requirements:
* Internet-accessible applications must prevent connections that originate in North Korea.
* Only members of a group named InfraSec must be allowed to configure network security groups (NSGs} and instances of Azure Firewall, VJM. And Front Door in Sub1.
* Administrators must connect to a secure host to perform any remote administration of the virtual machines. The secure host must be provisioned from a custom operating system image.
AWS Requirements
Fabrikam identifies the following security requirements for the data hosted in ContosoAWSV.
* Notify security administrators at Fabrikam if any AWS EC2 instances are noncompliant with secure score recommendations.
* Ensure that the security administrators can query AWS service logs directly from the Azure environment.
Contoso Developer Requirements
Fabrikam identifies the following requirements for the Contoso developers;
* Every month, the membership of the ContosoDevelopers group must be verified.
* The Contoso developers must use their existing contoso.onmicrosoft.com credentials to access the resources in Sub1.
* The Comoro developers must be prevented from viewing the data in a column named MedicalHistory in the ClaimDetails table.
Compliance Requirement
Fabrikam wants to automatically remediate the virtual machines in Sub1 to be compliant with the HIPPA HITRUST standard. The virtual machines in TestRG must be excluded from the compliance assessment.
NEW QUESTION # 159
Your company has a multi-cloud environment that contains a Microsoft 365 subscription, an Azure subscription, and Amazon Web Services (AWS) implementation. You need to recommend a security posture management solution for the following components:
* Azure loT Edge devices
* AWS EC2 instances
Which services should you include in the recommendation? To answer, select the appropriate options in the answer are a. NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 160
Hotspot Question
You have a Microsoft Entra tenant named contoso.com. You have 30 Azure subscriptions that are linked to contoso.com. The tenant contains the management groups shown in the following table.
You need to design a governance solution to manage access to all the Azure Storage accounts across the subscriptions. The solution must meet the following requirements:
- Use custom role-based access control (RBAC) to provide granular
access to control plane and data plane operations.
- Minimize administrative effort.
At which scope should you assign the roles, and what is the minimum number of assignments per role? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: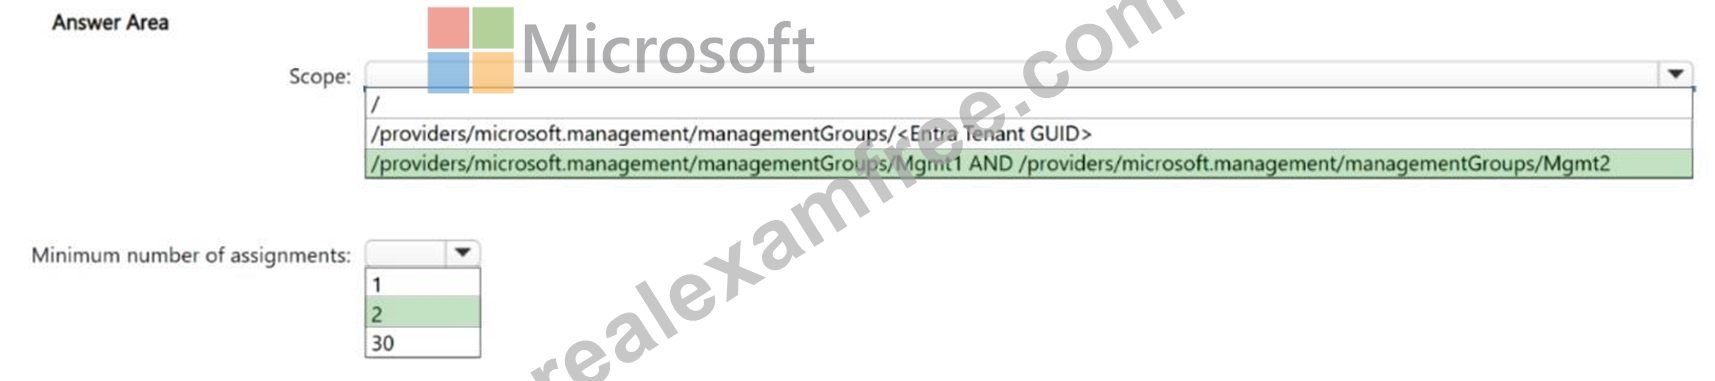
Explanation:
Box 1: ..Mgmt1 AND .. Mgmt2
For Microsoft Entra's two management groups, the appropriate scope for assigning roles is the management group level itself. This is because management groups are designed to be a broader scope for managing access and policies across multiple subscriptions.
Box 2: 2
Note:
Broadest Scope:
Management groups are the broadest scope in Azure, encompassing multiple subscriptions.
Reference:
https://learn.microsoft.com/en-us/azure/governance/management-groups/overview
NEW QUESTION # 161
Your on-premises network contains an Active Directory Domain Services (AD DS) domain and a hybrid deployment between a Microsoft Exchange Server 2019 organization and an Exchange Online tenant. The AD DS domain contains a group named Group1. Group1 is a member of the Organization Management role group for the Exchange deployment.
You have a Microsoft 365 E5 subscription that uses Microsoft Defender.
You have an Azure subscription that uses Microsoft Sentinel.
You need to recommend a solution to ensure that Group1 is marked as a sensitive group and that any changes made to Group1 raises an alert in Microsoft Sentinel. The solution must minimize administrative effort.
What should you include in the recommendation?
- A. Microsoft Entra Privileged Identity Management (PIM)
- B. Microsoft Defender for Office 365
- C. Microsoft Defender for Identity
- D. Microsoft Entra ID Protection
Answer: C
NEW QUESTION # 162
You are creating the security recommendations for an Azure App Service web app named App1.
App1 has the following specifications:
* Users will request access to App1 through the My Apps portal. A human resources manager will approve the requests.
* Users will authenticate by using Azure Active Directory (Azure AD) user accounts.
You need to recommend an access security architecture for App1.
What should you include in the recommendation? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Box 1 is the Azure AD Application https://docs.microsoft.com/en-us/azure/active-directory/develop
/quickstart-register-app
Box 2 is Access Package in Identity Governance
https://docs.microsoft.com/en-us/azure/active-directory/governance/entitlement-management-access-package- create
NEW QUESTION # 163
Your company is developing a new Azure App Service web app. You are providing design assistance to verify the security of the web app.
You need to recommend a solution to test the web app for vulnerabilities such as insecure server configurations, cross-site scripting (XSS), and SQL injection. What should you include in the recommendation?
- A. runtime application se/f-protection (RASP)
- B. interactive application security testing (IAST)
- C. dynamic application security testing (DAST)
- D. static application security testing (SAST)
Answer: C
Explanation:
Explanation
https://docs.microsoft.com/en-us/azure/security/develop/secure-develop#test-your-application-in-an-operating-st
NEW QUESTION # 164
You receive a security alert in Microsoft Defender for Cloud as shown in the exhibit. (Click the Exhibit tab.)
After remediating the threat which policy definition should you assign to prevent the threat from reoccurring?
- A. Azure Key Vault Managed HSM should have purge protection enabled
- B. Storage account keys should not be expired
- C. Storage account public access should be disallowed
- D. Storage accounts should prevent shared key access
Answer: C
Explanation:
Explanation
https://docs.microsoft.com/en-us/azure/storage/blobs/anonymous-read-access-prevent
NEW QUESTION # 165
You have a customer that has a Microsoft 365 subscription and uses the Free edition of Azure Active Directory (Azure AD)
The customer plans to obtain an Azure subscription and provision several Azure resources.
You need to evaluate the customer's security environment.
What will necessitate an upgrade from the Azure AD Free edition to the Premium edition?
- A. resource-based authorization
- B. Azure AD Multi-Factor Authentication
- C. role-based authorization
- D. Azure AD Privileged Identity Management (PIM)
Answer: C
NEW QUESTION # 166
Your company is developing an invoicing application that will use Azure Active Directory (Azure AD) B2C. The application will be deployed as an App Service web app. You need to recommend a solution to the application development team to secure the application from identity related attacks. Which two configurations should you recommend? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point.
- A. Azure AD workbooks to monitor risk detections
- B. Azure AD Conditional Access integration with user flows and custom policies
- C. custom resource owner password credentials (ROPC) flows in Azure AD B2C
- D. access packages in Identity Governance
- E. smart account lockout in Azure AD B2C
Answer: B,E
Explanation:
https://docs.microsoft.com/en-us/azure/active-directory-b2c/threat-management
https://docs.microsoft.com/en-us/azure/active-directory-b2c/conditional-access-user-flow?pivots=b2c-user-flow
Topic 2, Fabrikam, Inc
Overview
Fabrikam, Inc. is an insurance company that has a main office in New York and a branch office in Paris.
On-premises Environment
The on-premises network contains a single Active Directory Domain Services (AD DS) domain named corp.fabrikam.com.
Azure Environment
Fabrikam has the following Azure resources:
* An Azure Active Directory (Azure AD) tenant named fabrikam.onmicrosoft.com that syncs with corp.fabnkam.com
* A single Azure subscription named Sub1
* A virtual network named Vnet1 in the East US Azure region
* A virtual network named Vnet2 in the West Europe Azure region
* An instance of Azure Front Door named FD1 that has Azure Web Application Firewall (WAR enabled
* A Microsoft Sentinel workspace
* An Azure SQL database named ClaimsDB that contains a table named ClaimDetails
* 20 virtual machines that are configured as application servers and are NOT onboarded to Microsoft Defender for Cloud
* A resource group named TestRG that is used for testing purposes only
* An Azure Virtual Desktop host pool that contains personal assigned session hosts All the resources in Sub1 are in either the East US or the West Europe region.
Partners
Fabrikam has contracted a company named Contoso, Ltd. to develop applications. Contoso has the following infrastructure-.
* An Azure AD tenant named contoso.onmicrosoft.com
* An Amazon Web Services (AWS) implementation named ContosoAWS1 that contains AWS EC2 instances used to host test workloads for the applications of Fabrikam Developers at Contoso will connect to the resources of Fabrikam to test or update applications. The developers will be added to a security Group named Contoso Developers in fabrikam.onmicrosoft.com that will be assigned to roles in Sub1.
The ContosoDevelopers group is assigned the db.owner role for the ClaimsDB database.
Compliance Event
Fabrikam deploys the following compliance environment:
* Defender for Cloud is configured to assess all the resources in Sub1 for compliance to the HIPAA HITRUST standard.
* Currently, resources that are noncompliant with the HIPAA HITRUST standard are remediated manually.
* Qualys is used as the standard vulnerability assessment tool for servers.
Problem Statements
The secure score in Defender for Cloud shows that all the virtual machines generate the following recommendation-. Machines should have a vulnerability assessment solution.
All the virtual machines must be compliant in Defender for Cloud.
ClaimApp Deployment
Fabrikam plans to implement an internet-accessible application named ClaimsApp that will have the following specification
* ClaimsApp will be deployed to Azure App Service instances that connect to Vnetl and Vnet2.
* Users will connect to ClaimsApp by using a URL of https://claims.fabrikam.com.
* ClaimsApp will access data in ClaimsDB.
* ClaimsDB must be accessible only from Azure virtual networks.
* The app services permission for ClaimsApp must be assigned to ClaimsDB.
Application Development Requirements
Fabrikam identifies the following requirements for application development:
* Azure DevTest labs will be used by developers for testing.
* All the application code must be stored in GitHub Enterprise.
* Azure Pipelines will be used to manage application deployments.
* All application code changes must be scanned for security vulnerabilities, including application code or configuration files that contain secrets in clear text. Scanning must be done at the time the code is pushed to a repository.
Security Requirement
Fabrikam identifies the following security requirements:
* Internet-accessible applications must prevent connections that originate in North Korea.
* Only members of a group named InfraSec must be allowed to configure network security groups (NSGs} and instances of Azure Firewall, VJM. And Front Door in Sub1.
* Administrators must connect to a secure host to perform any remote administration of the virtual machines. The secure host must be provisioned from a custom operating system image.
AWS Requirements
Fabrikam identifies the following security requirements for the data hosted in ContosoAWSV.
* Notify security administrators at Fabrikam if any AWS EC2 instances are noncompliant with secure score recommendations.
* Ensure that the security administrators can query AWS service logs directly from the Azure environment.
Contoso Developer Requirements
Fabrikam identifies the following requirements for the Contoso developers;
* Every month, the membership of the ContosoDevelopers group must be verified.
* The Contoso developers must use their existing contoso.onmicrosoft.com credentials to access the resources in Sub1.
* The Comoro developers must be prevented from viewing the data in a column named MedicalHistory in the ClaimDetails table.
Compliance Requirement
Fabrikam wants to automatically remediate the virtual machines in Sub1 to be compliant with the HIPPA HITRUST standard. The virtual machines in TestRG must be excluded from the compliance assessment.
NEW QUESTION # 167
Hotspot Question
You have an Azure subscription that contains Azure App Service apps. The apps have the following characteristics:
- The apps are deployed by using continuous integration and continuous
deployment (CI/CD) pipelines in Azure DevOps.
- The apps are deployed to a test environment first, and then to a
production environment.
- The source code for the apps is stored in Azure Repos.
You plan to implement DevSecOps controls based on the Microsoft Cloud Adoption Framework for Azure.
You need to recommend testing controls to meet the following requirements:
- All the source code must be tested for security vulnerabilities in
Azure Repos before deploying the apps.
- Once the apps are deployed to the test environment, they must be
tested for security vulnerabilities.
Which testing method should you recommend for each stage? To answer, select the options in the answer area.
NOTE: Each correct answer is worth one point.
Answer:
Explanation:
Explanation:
Box 1: Static application security testing (SAST
All the source code must be tested for security vulnerabilities in Azure Repos before deploying the apps.
SAST (Static Application Security Testing) SAST tools analyze source code or bytecode early in the pipeline to identify security flaws before deployment. They provide deep insights into insecure coding patterns and vulnerabilities by scanning code syntax and data flows without executing the program.
Box 2: Dynamic Application Security Testing (DAST)
Once the apps are deployed to the test environment, they must be tested for security vulnerabilities.
Dynamic Application Security Testing (DAST) is the process of analyzing a web application through the front-end to find vulnerabilities through simulated attacks. This type of approach evaluates the application from the "outside in" by attacking an application like a malicious user would. After a DAST scanner performs these attacks, it looks for results that are not part of the expected result set and identifies security vulnerabilities.
Reference:
https://learn.microsoft.com/en-us/security/benchmark/azure/security-controls-v3-devops-security
NEW QUESTION # 168
You have an Azure subscription.
You have a DNS domain named contoso.com that is hosted by a third-party DNS registrar.
Developers use Azure DevOps to deploy web apps to App Service Environments. When a new app is deployed, a CNAME record for the app is registered in contoso.com.
You need to recommend a solution to secure the DNS record for each web app. The solution must meet the following requirements:
- Ensure that when an app is deleted, the CNAME record for the app is
removed also.
- Minimize administrative effort.
What should you include in the recommendation?
- A. Microsoft Defender for DNS
- B. Microsoft Defender for Cloud Apps
- C. Microsoft Defender for DevOps
- D. Microsoft Defender for App Service
Answer: D
Explanation:
Defender for App Service identifies any DNS entries remaining in your DNS registrar when an App Service website is decommissioned - these are known as dangling DNS entries.
https://learn.microsoft.com/en-us/azure/defender-for-cloud/defender-for-app-service- introduction#dangling-dns-detection Microsoft Defender for DNS provides an additional layer of protection for resources that use Azure DNS's Azure-provided name resolution capability.
https://learn.microsoft.com/en-us/azure/defender-for-cloud/defender-for-app-service- introduction#dangling-dns-detection
NEW QUESTION # 169
You are designing a security operations strategy based on the Zero Trust framework.
You need to increase the operational efficiency of the Microsoft Security Operations Center (SOC).
Based on the Zero Trust framework, which three deployment objectives should you prioritize in sequence? To answer, move the appropriate objectives from the list of objectives to the answer area and arrange them in the correct order.
Answer:
Explanation:
1 - Establish visibility.
2 - Enable additional protection and detection control.
3 - Enable automation.
NEW QUESTION # 170
Your company plans to deploy several Azure App Service web apps. The web apps will be deployed to the West Europe Azure region. The web apps will be accessed only by customers in Europe and the United States.
You need to recommend a solution to prevent malicious bots from scanning the web apps for vulnerabilities.
The solution must minimize the attach surface.
What should you include in the recommendation?
- A. network security groups (NSGs)
- B. Azure Firewall Premium
- C. Azure Application Gateway Web Application Firewall (WAF)
- D. Azure Traffic Manager and application security groups
Answer: C
NEW QUESTION # 171
Your company has an on-premise network in Seattle and an Azure subscription. The on-premises network contains a Remote Desktop server.
The company contracts a third-party development firm from France to develop and deploy resources to the virtual machines hosted in the Azure subscription.
Currently, the firm establishes an RDP connection to the Remote Desktop server. From the Remote Desktop connection, the firm can access the virtual machines hosted in Azure by using custom administrative tools installed on the Remote Desktop server. All the traffic to the Remote Desktop server is captured by a firewall, and the firewall only allows specific connections from France to the server.
You need to recommend a modern security solution based on the Zero Trust model. The solution must minimize latency tor developers.
Which three actions should you recommend? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Configure Azure Active Directory (Azure AD) Conditional Access with multi-factor authentication (MFA) and named locations.
- B. Implement Azure Firewall to restrict host pool outbound access.
- C. Configure network security groups (NSGs) to allow access from only specific logical groupings of IP address ranges.
- D. Deploy a Remote Desktop server to an Azure region located in France.
- E. Migrate from the Remote Desktop server to Azure Virtual Desktop.
Answer: A,B,E
NEW QUESTION # 172
You have a Microsoft 365 E5 subscription.
You plan to deploy Global Secure Access universal tenant restrictions v2.
Which authentication plane resources and which data plane resources will be protected? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
NEW QUESTION # 173
You are designing the security standards for a new Azure environment.
You need to design a privileged identity strategy based on the Zero Trust model.
Which framework should you follow to create the design?
- A. Microsoft Security Development Lifecycle (SDL)
- B. Rapid Modernization Plan (RaMP)
- C. Enhanced Security Admin Environment (ESAE)
- D. Microsoft Operational Security Assurance (OSA)
Answer: B
Explanation:
https://docs.microsoft.com/en-us/security/compass/security-rapid-modernization-plan This rapid modernization plan (RAMP) will help you quickly adopt Microsoft's recommended privileged access strategy.
NEW QUESTION # 174
You need to recommend a solution to meet the AWS requirements.
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 175
Your company has a Microsoft 365 E5 subscription.
The Chief Compliance Officer plans to enhance privacy management in the working environment. You need to recommend a solution to enhance the privacy management. The solution must meet the following requirements:
* Identify unused personal data and empower users to make smart data handling decisions.
* Provide users with notifications and guidance when a user sends personal data in Microsoft Teams.
* Provide users with recommendations to mitigate privacy risks.
What should you include in the recommendation?
- A. communication compliance in insider risk management
- B. Privacy Risk Management in Microsoft Priva
- C. Advanced eDiscovery
- D. Microsoft Viva Insights
Answer: B
Explanation:
Privacy Risk Management in Microsoft Priva gives you the capability to set up policies that identify privacy risks in your Microsoft 365 environment and enable easy remediation. Privacy Risk Management policies are meant to be internal guides and can help you: Detect overexposed personal data so that users can secure it. Spot and limit transfers of personal data across departments or regional borders. Help users identify and reduce the amount of unused personal data that you store.
https://www.microsoft.com/en-us/security/business/privacy/microsoft-priva-risk-management
NEW QUESTION # 176
......
Microsoft SC-100, also known as the Microsoft Cybersecurity Architect certification exam, is a globally recognized certification that validates the skills and knowledge required to design and implement secure solutions using Microsoft technologies. Microsoft Cybersecurity Architect certification exam is intended for those professionals who want to take their career in cybersecurity to the next level and demonstrate their expertise in designing, implementing, and maintaining secure systems.
Online Questions - Valid Practice SC-100 Exam Dumps Test Questions: https://www.realexamfree.com/SC-100-real-exam-dumps.html
100% Real SC-100 dumps - Brilliant SC-100 Exam Questions PDF: https://drive.google.com/open?id=165hRhXLGx7mkfKCfzL86nqNp0e8yLVfO
